From a root shell run
dd if=/dev/block/by-name/nvdata of=/sdcard/nvdata.img
Then you should have nvdata.img in internal storage.
The phone must be rooted? Or I can put in the system so it will work without root?
@ars18 ty for reverse engineering the crypto! I wonder if you looked into bt address and wifi mac as well?
Additionally, thought it would be nice to add an IMEI generator to the app, going to dump my research here.
Graphic credit imei.info link below
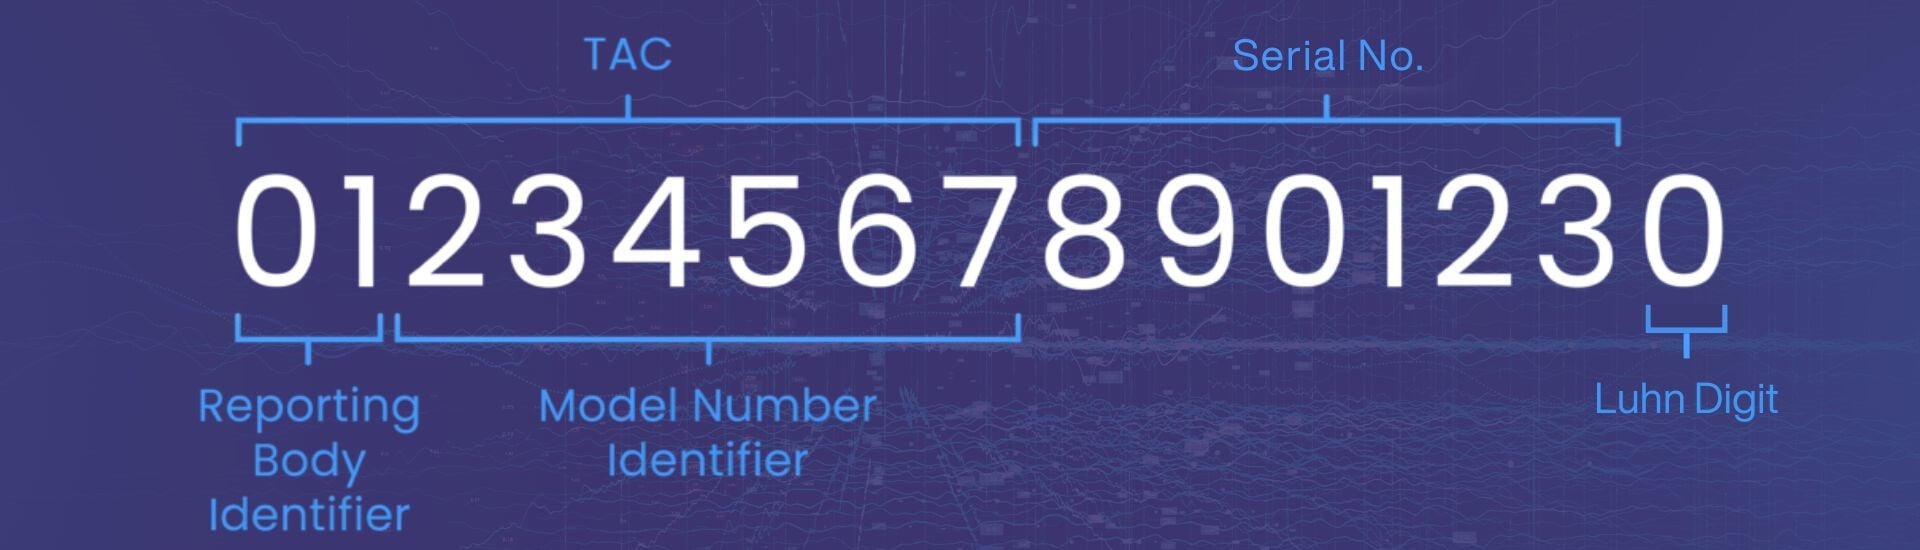
IMEI is structured in 3 parts:
-
TAC (Type Allocation Code) First 8 Digits. The first two digits identify cert. region (01 is US), next 6 identify manufacturer and model. For instance, all Kyocera E4810 should start with 01558800, 01 for USA, 558800 for Kyocera E4810.
-
SNR (Serial number) 6 digits that uniquely identify your device.
-
CD (Check Digit) 1 digit that is calculated from the preceding 14 using Luhn (mod 10) algo. (Implemented in attached python script)
Info on the structure of IMEI mainly from here:
Here is an extensive list of TAC codes that can be parsed in to an offline DB.
TACS can also be sourced here:
So a basic generator would allow you to choose a known TAC, (like 01558800 for Kyocera E4810 for example), generate a random 6 digit number (like say, um, 123456) and calculate a luhn for that (which happens to be 3 for this example. Following the examples, the resulting IMEI would be 01558800 - 123456 - 3).
Here is a python script that checks IMEI numbers. It contains a function to generate the luhn check digit, as well as a very tiny hardcoded tac db.
import sys

# Tiny hardcoded TAC DB
TAC_DB = {
  "35875110": "Apple iPhone 11",
  "35299209": "Apple iPhone 8",
  "35744105": "Samsung Galaxy S4",
  "35903908": "Samsung Galaxy S8",
  "35174605": "Google Galaxy Nexus",
  "35824005": "Google Nexus 5",
  "35447909": "Nokia 1",
  "35151304": "Nokia E72-1",
  "01558800": "Kyocera Dura Extreme E4810"
}

# Reporting Body Identifiers (First 2 digits)
RBI_MAP = {
  "01": "CTIA (USA)",
  "35": "BABT (UK/Global)",
  "86": "TAF (China)",
  "91": "MSAI (India)",
  "99": "GHA (Multi-RAT / Global)"
}

def calculate_luhn(number_str):
#Calculates the expected 15th digit for a 14-digit sequence.
  digits = [int(d) for d in number_str]
  total_sum = 0
  for i, digit in enumerate(digits):
    if i % 2 != 0:
        doubled = digit * 2
        total_sum += (doubled - 9) if doubled > 9 else doubled
    else:
        total_sum += digit
  return (10 - (total_sum % 10)) % 10

def analyze_imei(imei):
  imei = imei.strip().replace(" ", "").replace("-", "")
  if len(imei) != 15 or not imei.isdigit():
    return f"Error: {imei} is not a valid 15-digit IMEI format."
  tac = imei[:8]
  rbi = imei[:2]
  serial = imei[8:14]
  check_digit = int(imei[14])

  # Analysis
  region = RBI_MAP.get(rbi, "Unknown / Other Body")
  model = TAC_DB.get(tac, "Model not in local database")
  expected_luhn = calculate_luhn(imei[:14])
  luhn_status = "VALID" if expected_luhn == check_digit else f"INVALID (Expected {expected_luhn})"

  result = [
    f"\n--- Analysis for: {imei} ---",
    f"  [+] Region (RBI):  {rbi} -> {region}",
    f"  [+] Make/Model:    {model} (TAC: {tac})",
    f"  [+] Device Serial: {serial}",
    f"  [+] Luhn Check:    {luhn_status}",
  ]

  return "\n".join(result)

if _name_ == “_main_”:

# Check if arguments were passed
if len(sys.argv) < 2:
    print("Usage: python imei_analyzer.py <imei1> <imei2> ...")
    print("Example: python imei_analyzer.py 358751101234567 357441051234560")
else:
    for arg in sys.argv[1:]:

        print(analyze_imei(arg))
Try the script using our above E4810 example:
python imei_checker.py 015588001234563
You can also test with an invalid luhn by changing the last digit randomly.
This info can easily be used to implement a basic IMEI generator in the app that should allow for a basic “verizon” (using a known TAC) or other IMEI.
THIS POST IS FOR EDUCATIONAL PURPOSES Changing an IMEI can be unethical and illegal in your area. The poster declaims any responsibility for your actions.
Wow cool research.
How about building in imei.info so that the user can pick a phone and the app will pull a imei from that site. Obviously the app will need access to the internet (as opposed to @sh7411usa’s idea…).
Wdym put in system? You’re building a ROM and wanna make it w system app? That should work too cuz system apps have root access but I don’t know
Thanks so much for the research! I love the idea! I’ll try to add it later today.
Done!
https://github.com/flipphoneguy/mtk-imei-switcheroo-app
I used an iphone that’s sold in the US for Verizon
Can also generate kosher IMEIs (for Israeli kosher SIMs). Got the list from cellular Israel
I tested basic functionality. I didn’t test Verizon or kosher SIM.
Lmk if there’s any issues
Amazing!! Can’t wait to test it out! 
I’d suggest one more feature: Add a launch method via dialer code (you can do *#*#1122#*#* like some other devices), and an option to hide the app from the launcher. This will be perfect for including as a system app in a ROM. Although I understand that including in a non rooted ROM will require using changing your access approach to priv-app instead of su runtime (because su is not included in non rooted roms, obviously).
Also - large size TAC db available for easy CSV download here:
I found that. First of all that doesn’t have kosher numbers and secondly I didn’t want my app being a few mb. I love a few kb!
Regarding building into ROM, I’m not sure if anyone would use that. And if yes, someone building a ROM should be able to do it themselves. The only things he’ll have to change is that you mentioned. It’s open source after all (it maybe it’s just that I’m lazy  )
mtkclient would be best option if that’s easy for you.
Partitions I need to claim full repo support:
- nvram
- nvdata
- nvcfg
- md1img
But don’t upload publicly, will have your imei in it.
I started, but didn’t know if it would vary with multiple devices so I put it on hold for now. Perhaps no difference.
How important is it?
Nice idea. Will definitely leave that to the @flipphoneguy app.
I’m also nervous to add something too suggestive for actually switching I’m already getting hit too hard with the gplay repo.
I see he did it already
With root, system app no issue. But without… You will need multiple edits to the app and I really feel like selinux will not be a fun time.
For roms that have root would be great as default included.
Not mammesh vichtig, just an idea.
No, it won’t. Like really. However - it would be similar to ROM development in general. Lots of trial and error and AI prompts. But, as the wise man once said:
Point is, for shleimus, I thought it would be nice to include the app in 613, with the ability to restore IMEI, Wi-Fi mac, and BT address.
In conclusion:
You will notice that I haven’t offered to do it myself. 
Gotcha. Yeah, that should be simple enough. I’ll try and figure it out. I will have to label each phone process separate unless I can prove all supported so far is the same, or have anecdotal evidence from others.
If you figure out the F21, I can check for you on some other MTK devices.
I found that on my device it’s plain bytes. Not encoded at all! Just 2 weird bytes aa XX where it’s always aa and the XX is different in every file (bt Mac gps). I’ve seen on XDA someone saying he modified those files and it didn’t persist in reboot. Maybe it got corrupted so went back to factory. I can try later today on my phone. I also don’t know if this is just my phone or app MT67xxx